What the platform does
Four features carry the product: the credential vault, the policy engine, agent identity, and approvals.
Proxied calls keep credentials out of your agents' hands
OAuth tokens and API keys live in the vault as one managed copy, encrypted at rest. The SDK sends the provider request to Alter; the vault injects the credential on the way out and returns the provider response. Proxied calls keep secrets out of your code, your prompts, and your database, and proxy-only agent keys make the proxy the only path.
- 70+ OAuth providers and 70+ managed secret templates behind one request call
- Works identically for user-authorized OAuth grants and operator-provisioned secrets
- Two runtime modes: retrieve in-process, or full proxy on Alter's side
import osfrom alter_sdk import App, HttpMethod, PendingApproval async with App(api_key=os.environ["ALTER_API_KEY"]) as app: # Token resolved, injected, and audited automatically response = await app.proxy_request( HttpMethod.GET, "https://api.github.com/user/repos", grant_id=os.environ["GITHUB_GRANT_ID"], query_params={"sort": "updated", "per_page": 5}, ) if isinstance(response, PendingApproval): response = await app.await_approval(response.approval_id) repos = response.body_json()Default deny. Down to the parameter.
Rules compose from the organization down to a single connection and are evaluated as each request happens. Beyond scopes, time windows, IP ranges, and rate quotas, content rules inspect the operation itself: deny outbound email to external recipients, redact a field instead of blocking the call, require a fresh sign-in, or hold payments over a threshold for a human.
- Method and endpoint restrictions per grant
- Parameter-level content rules: deny, redact, or step up
- Simulate a rule against a real request shape before committing it
All runtime policies
Every custom runtime policy in this app, across all levels. Select a row to inspect its full definition and target.
Support Bot only emails customers
Agent runtime policy · Support Bot
Level
Agent
Target
Support Bot · support-bot
Applies to
Requests from this agent
Provider
Gmail · OAuth
Matching requests are refused before the provider is called.
Request conditions (all must match)
- Operation
- gmail.users.messages.send
- HTTP method
- POST
- Endpoint
- /gmail/v1/users/me/messages/send
- Parameter
- to does not end with @acme.example
- Effect
- Deny
- Message
- "Support Bot may only email acme.example addresses."
Explain a request
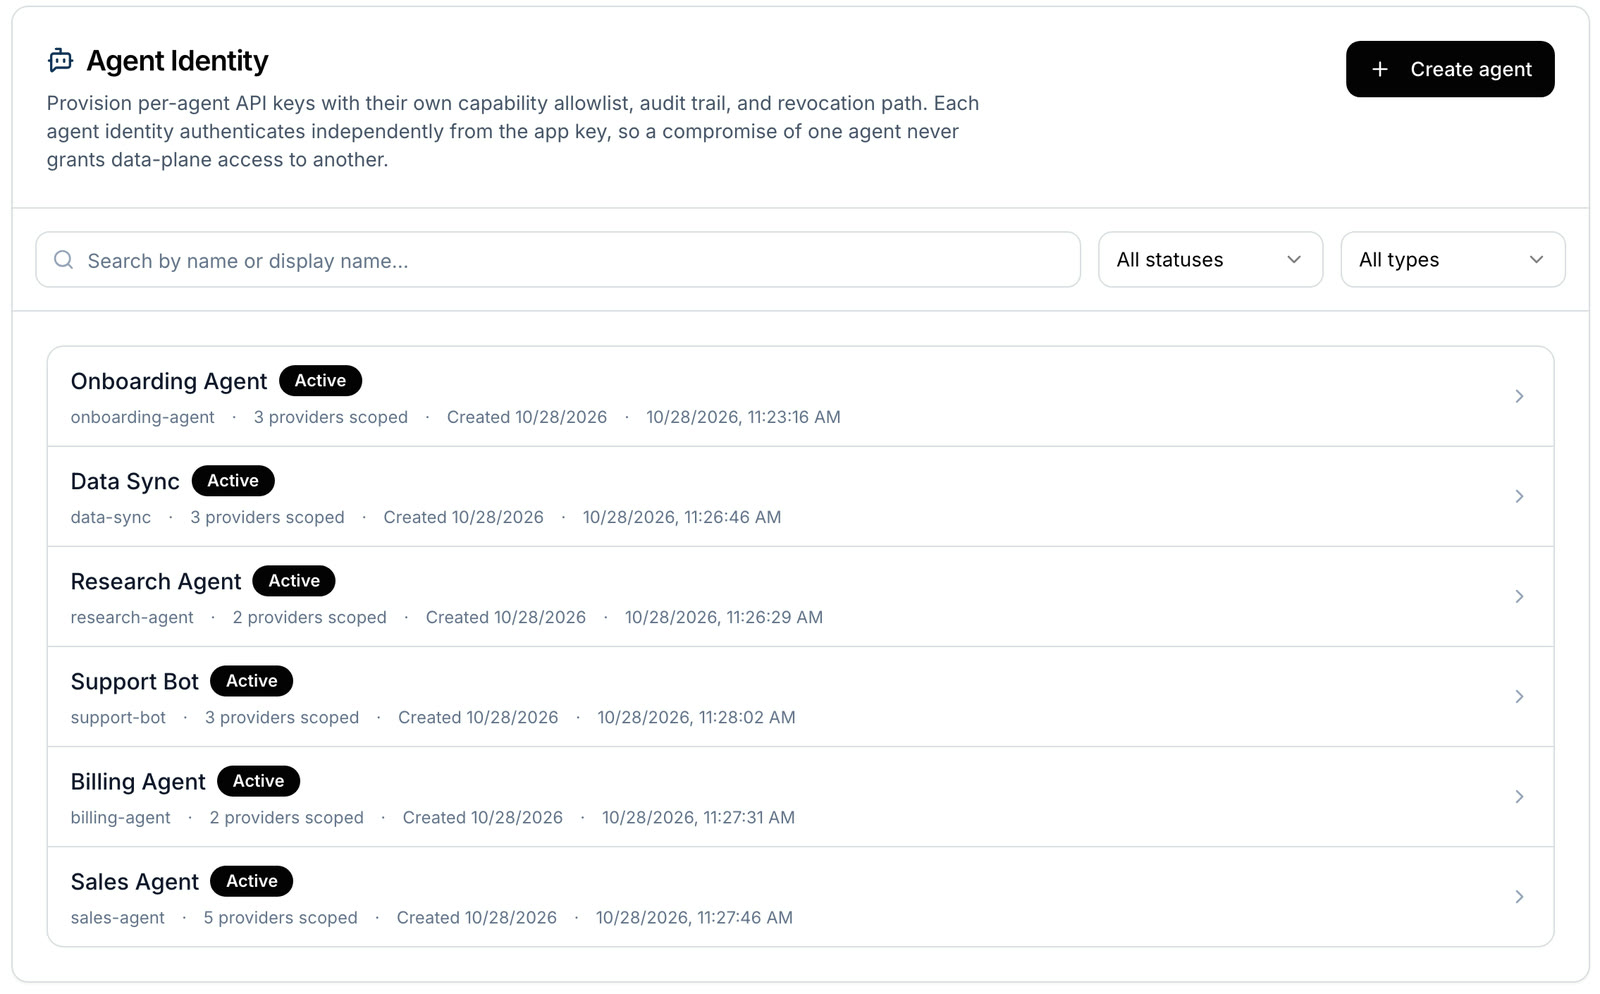
Every agent gets its own identity
Register an agent once and mint it a key scoped to exactly what it needs; revoking one never touches another. Before any call runs, Alter resolves the whole chain: organization, application, end user, agent. Your identity provider decides who exists; with Okta, Auth0, WorkOS, or Clerk webhooks enabled, deprovisioning cascades in real time.
- Per-agent keys with narrowed scopes
- Delegation traceable back to a real person
- Okta, Auth0, WorkOS, Clerk, or any OIDC provider
Sensitive calls wait for a person
Policy decides which calls need review: by provider, agent, connection, or condition, down to only payments over a threshold. The gated call is frozen and integrity-checked, the agent gets a pending result immediately, and a named approver decides from the Wallet. What they reviewed is what executes.
- The agent polls or awaits the outcome; everything else keeps flowing
- Approvers are named on the policy, not hardcoded in application code
- Approvals and denials both land in the audit trail
Pending approvals
POST api.stripe.com/v1/refunds
Expires Oct 29, 2:03 PMRefund duplicate annual charge for Initech (ticket #4907)
Provider: stripe · billing-agent
No approvals are waiting on you.
Recent decisions
Back to approvals
Acme Assist asked to do something that needs your OK. Nothing happens unless you approve.
Approval request
PendingExpires 10/29/2026, 2:03:05 PM
What the agent wants to do
POST api.stripe.com/v1/refunds
Provider
stripe
Grant type
Managed Secret
Grant label
billing-agent
Request values
- body.charge
- "ch_3Pf8a1b2c3d4e5f6a7b8c9d0"
- body.amount
- 24000
- body.reason
- "requested_by_customer"
- body.metadata.account
- "Initech"
Reason given
Refund duplicate annual charge for Initech (ticket #4907)
Approve this request?
The agent will be able to execute the request below.
POST api.stripe.com/v1/refunds
Request values
- body.charge
- "ch_3Pf8a1b2c3d4e5f6a7b8c9d0"
- body.amount
- 24000
- body.reason
- "requested_by_customer"
- body.metadata.account
- "Initech"
This action is recorded in the audit log with your identity.
Reason (optional)
More features
Credential preflight
Credentials are validated against the provider at save time. A bad key fails the save, not the first production call.
Automatic token refresh
Expired tokens refresh server-side before the request goes out.
Rotation without redeploys
Rotate a managed secret once; every consumer picks it up on the next request.
Delegation chains
When agents act for users or other agents, the full chain is recorded.
Directory sync
Okta, Auth0, WorkOS, and Clerk, with automatic deprovisioning. Any OIDC provider for sign-in.
Time windows and IP allowlists
Bound access to working hours and known networks.
Rate quotas
Per-caller call budgets, with a retry-after when the window is spent.
Policy simulation
Test a rule against a request shape before you commit it.
Provider API discovery
Cataloged operations per provider, queryable by agents at runtime.
Put your agents under privileged access control.
Book a 30-minute walkthrough with the founders.